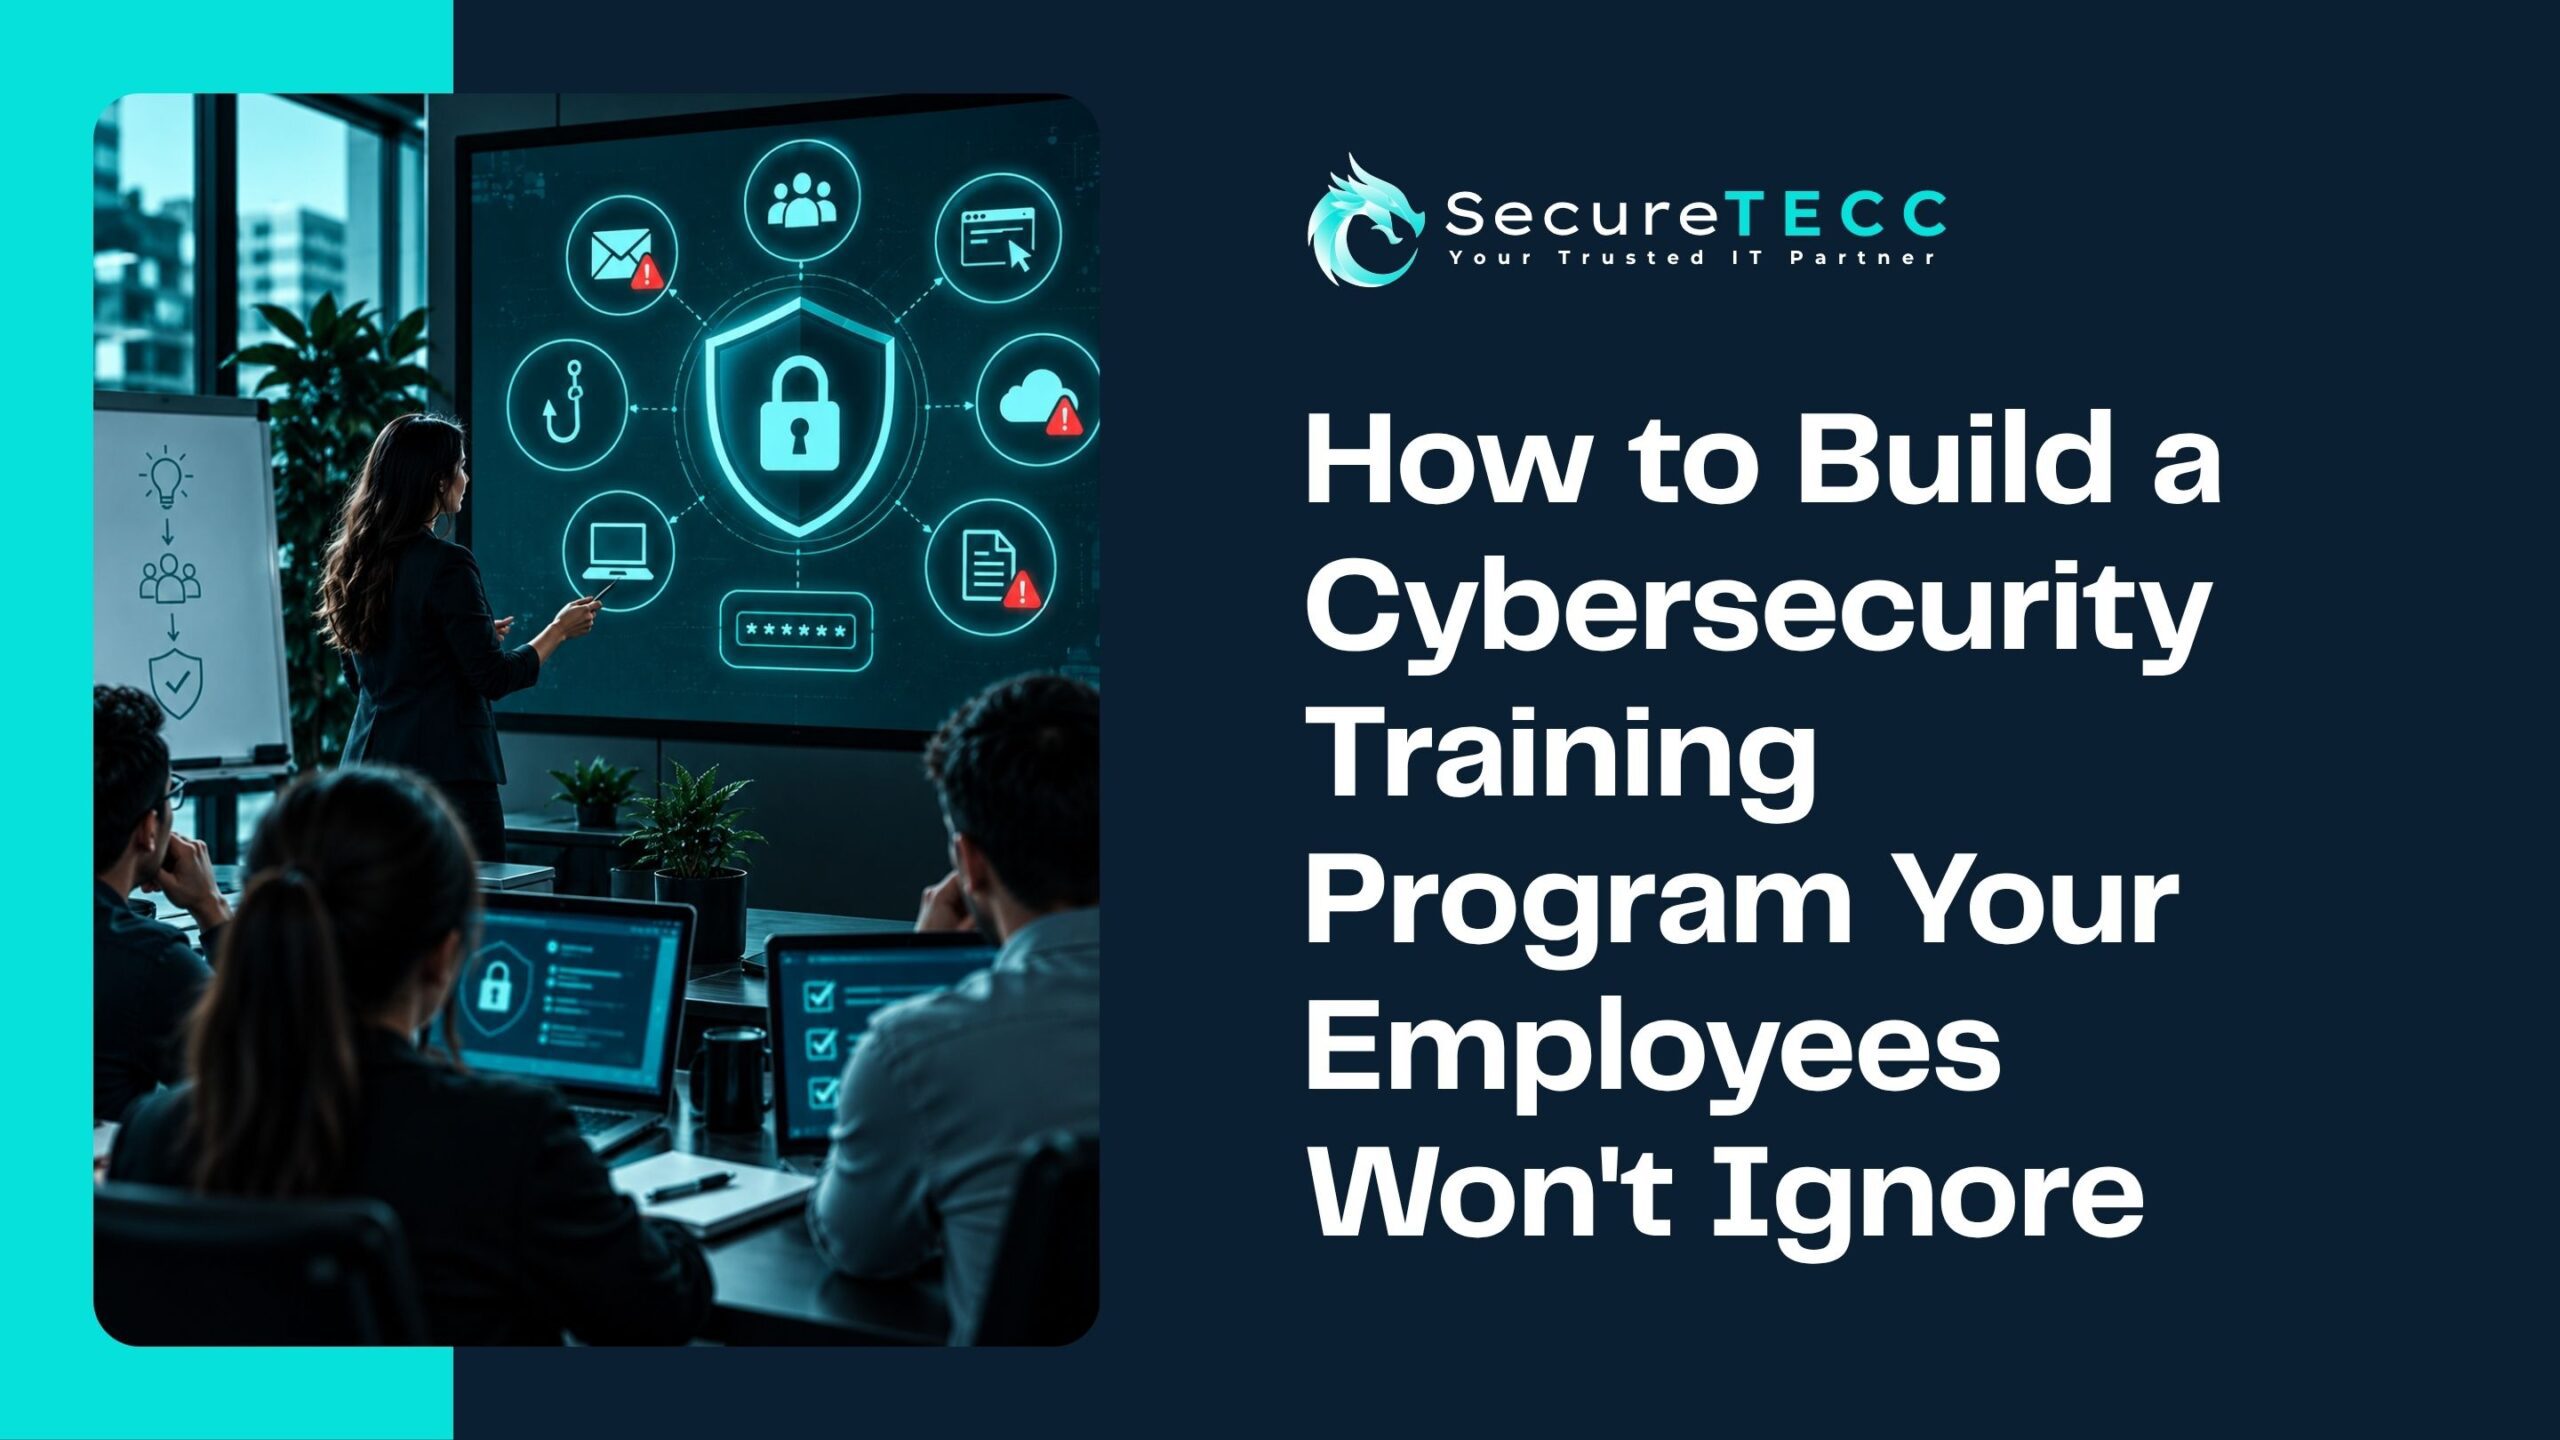
Once a year, an email goes out: “Please complete your annual security training by Friday.” Everyone clicks through a slideshow, answers a few quiz questions on autopilot, and gets their completion certificate. Six months later, the same team member clicks a phishing link that looks almost exactly like what the training warned about.
This isn’t a training content problem — it’s a training design problem. Most cybersecurity training programs are built to satisfy a compliance checkbox, not to actually change behavior, and there’s a real difference between the two. Here’s why most programs get ignored, and what actually builds a program employees engage with instead of tolerate.
Why Do Most Cybersecurity Training Programs Get Ignored?
Most training programs get ignored because they’re built around a single annual session rather than ongoing reinforcement, use generic content that doesn’t reflect real threats an employee will actually face, and measure success by completion rates rather than actual behavior change. A program built this way satisfies a compliance requirement without meaningfully reducing risk.
What Does the Research Actually Say About Training Effectiveness?
There’s a real, measurable gap between programs that work and programs that just check a box. According to KnowBe4’s 2026 Phishing by Industry Benchmarking Report — based on data from over 64,000 organizations — a full year of continuous, reinforced security awareness training reduces phishing susceptibility from a baseline of roughly 33% down to around 4%, an 87% reduction. But that result depends entirely on sustained reinforcement: peer-reviewed research published through USENIX has found that the benefits of a one-time training session largely fade within about six months without ongoing reinforcement.
In other words, the “annual training” model isn’t just less effective — the research suggests its impact is mostly gone well before the next year’s session even happens.
1. Make It Frequent, Not Annual
Frequency is consistently one of the strongest predictors of whether a training program actually changes behavior, more so than the depth or production value of any single module. Short, regular touchpoints — a few minutes a month rather than one long session a year — build habits in a way an annual event simply can’t.
2. Use Realistic Simulations, Not Just Slideshows
Watching a video about phishing and actually encountering a realistic simulated phishing email in your own inbox are very different experiences — only one of them tests whether the learning actually transferred. Regular, unannounced phishing simulations, paired with immediate, judgment-free feedback when someone clicks, do far more to build real recognition skills than passive content ever will.
3. Build a No-Blame Reporting Culture
One of the most overlooked pieces of an effective program isn’t preventing every click — it’s making sure people report suspicious activity quickly when it does happen. Industry data consistently shows that only a small fraction of employees who click a phishing link actually report it, largely out of embarrassment or fear of consequences. A program that treats a reported near-miss as a win, not a confession, closes that gap significantly — and a well-designed behavior-focused program can drive reporting rates meaningfully higher than a standard, completion-only compliance approach.
4. Tailor Content to Actual Roles
A finance team member handling wire transfers faces a genuinely different risk profile than someone in a warehouse role with no access to financial systems — yet most off-the-shelf training treats every employee identically. Training that reflects the specific scenarios a role actually encounters (business email compromise for finance and accounting staff, credential security for anyone with system access, physical security awareness for on-site roles) lands as relevant instead of generic, and relevant content is what people actually remember.
5. Get Leadership Visibly Involved
When training is something leadership visibly participates in — not just mandates from a distance — it signals the program is a genuine priority rather than a compliance formality being pushed downward. An executive who’s willing to be included in simulated phishing tests, and occasionally shares their own near-miss story, does more for a program’s credibility than any policy memo.
6. Track Real Metrics, Not Just Completion Rates
Completion rate answers one question: did people click through the training? It says nothing about whether behavior actually changed. A program built to actually work tracks metrics that reflect real outcomes — click rates on simulated phishing tests, how quickly suspicious messages get reported, and whether repeat-offender rates are trending down over time. These numbers tell you whether the program is working; completion certificates alone don’t.
What Does a Program Like This Actually Look Like Month to Month?
Picture a 25-person company shifting away from their old once-a-year training video. Instead, employees now get a short, five-minute training module monthly, an unannounced simulated phishing test roughly every few weeks, and a simple internal recognition — nothing elaborate — when someone correctly reports a suspicious email. Within the first six months, their internal click rate on simulated tests drops noticeably, and more importantly, actual reporting of suspicious real-world emails increases, because employees no longer feel embarrassed to flag something that turned out to be nothing.
How SecureTECC Approaches This
SecureTECC’s Cybersecurity services include employee awareness support built around this same principle — ongoing engagement rather than a single annual event — paired with the technical backstops (MFA, monitoring, email security) that catch what training alone inevitably misses. A training program and a technical safety net work best together, not as substitutes for one another.
Frequently Asked Questions
How often should cybersecurity training actually happen?
Monthly or more frequent touchpoints consistently outperform an annual session, since frequency is one of the strongest predictors of whether training actually changes behavior rather than just satisfying a compliance requirement.
Isn’t punishing repeat phishing-simulation failures a fair way to enforce accountability?
It tends to backfire — a punitive approach discourages honest, timely reporting, which matters more for actual security than eliminating every single click. A program focused on coaching and recognition typically outperforms one built around penalties.
Do small businesses really need a structured training program, or is basic awareness enough?
Given that the vast majority of breaches still involve some human element, even a lightweight structured program — short monthly content and occasional simulations — meaningfully outperforms a single annual session, regardless of company size.
How do we know if our current training program is actually working?
Look past completion rates to the metrics that reflect real behavior: are simulated phishing click rates trending down over time, and is reporting of suspicious messages actually increasing? Those two numbers tell you far more than a stack of completion certificates.
Should training content be the same for every employee?
Generally not — content tailored to a role’s actual risk exposure (financial staff, system administrators, general staff) tends to be more memorable and relevant than a one-size-fits-all module applied uniformly across the company.
The Bottom Line
A cybersecurity training program that gets ignored isn’t a failure of your employees — it’s usually a sign the program itself was built to satisfy a checkbox rather than change behavior. Frequency, realistic practice, a no-blame reporting culture, and real metrics are what separate a program people tune out from one that actually holds up when a real attack arrives.
Want help building a training program that actually sticks, rather than one more annual video? Book a free consultation with SecureTECC Solutions — no pressure, no obligation.